
Image: Unsplash.
Most "Articles 9-15 templates" skip the question that decides your workload: are you the provider or the deployer? Articles 9 to 15 set the requirements a high-risk AI system must meet, and Article 16 puts them on the provider: "ensure that their high-risk AI systems are compliant with the requirements set out in Section 2." If you buy or license an Annex III system, your own duties are in Article 26. The templates below cover each article and say who owns it.
Check scope first. Our Annex III high-risk AI systems guide covers the category definitions, and the EU AI Act compliance guide for small teams walks through the scoping analysis.
The dates that matter
| What | Applies from | Who |
|---|---|---|
| Prohibited practices (Article 5) | February 2, 2025 | Everyone |
| Two new prohibitions added by the AI Omnibus (non-consensual intimate imagery, child sexual abuse material) | December 2, 2026 | Everyone |
| GPAI model obligations | August 2, 2025 (models already on the market: August 2, 2027) | Model providers |
| High-risk rules for Annex III systems (Articles 9-15, 26) | December 2, 2027 | Providers and deployers |
| High-risk rules for Annex I product systems | August 2, 2028 | Providers and deployers |
All five come from Article 113 of the consolidated text. If the system you deploy runs on a general-purpose model, the model provider's documentation duties already apply, so ask for that documentation now.
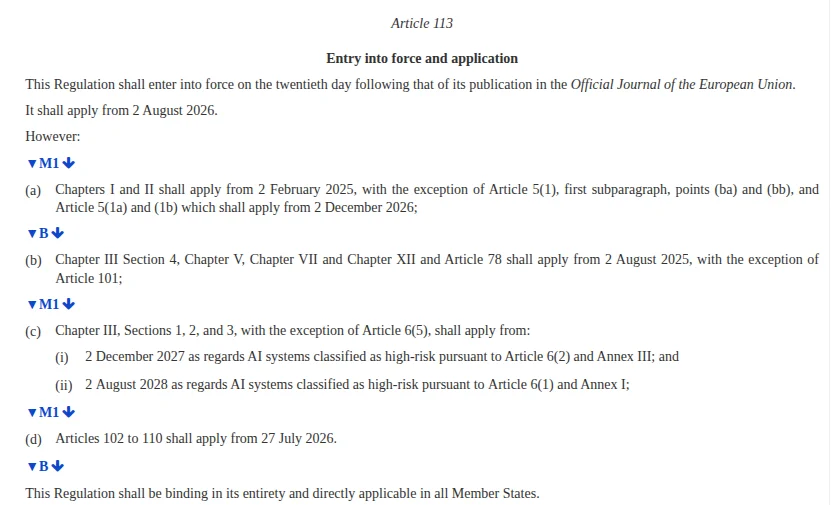
Screenshot: Regulation (EU) 2024/1689, Article 113, consolidated version of July 27, 2026, EUR-Lex.
Who owns what: provider vs deployer
| Article | Provider's duty | What the deployer does |
|---|---|---|
| 9 Risk management | Runs the risk management system across the lifecycle | Monitors operation per the instructions and reports risks (Article 26(5)); keeps its own risk record |
| 10 Data governance | Training, validation and testing data | Makes sure input data it controls is relevant and sufficiently representative (Article 26(4)) |
| 11 Technical documentation | Writes it to Annex IV, keeps it 10 years (Article 18) | Keeps a copy on file |
| 12 Record-keeping | Builds automatic logging into the system | Keeps logs under its control for at least six months (Article 26(6)) |
| 13 Transparency | Supplies instructions for use | Uses the system per those instructions (Article 26(1)) |
| 14 Human oversight | Designs the system so people can oversee it | Assigns oversight to people with "the necessary competence, training and authority" (Article 26(2)) |
| 15 Accuracy and robustness | Declares accuracy levels and secures the system | Monitors performance and suspends use if it presents a risk (Article 26(5)) |
Two more deployer duties that small teams miss: employers must tell workers' representatives and affected workers before a high-risk system is used at the workplace (Article 26(7)), and deployers of Annex III systems that make or help make decisions about people must tell those people (Article 26(11)). Public bodies, private entities providing public services, and deployers using AI for credit scoring or life and health insurance pricing must also complete a fundamental rights impact assessment before first use (Article 27).
The scope of that last duty trips people up. An April post on r/gdpr told DPOs that deployers of high-risk AI must do a fundamental rights impact assessment before use. u/Comfortable-Fall1419 pushed back that the post was wrong on points, and the author, u/ales-on-reddit, conceded: "I wrote it too broadly. General deployer obligations under Article 26 are much lighter." The assessment applies to the Article 27 groups, not to every deployer.
https://www.reddit.com/r/gdpr/comments/1sesenc/ai_act_deployer_obligations_that_most_dpos_are/
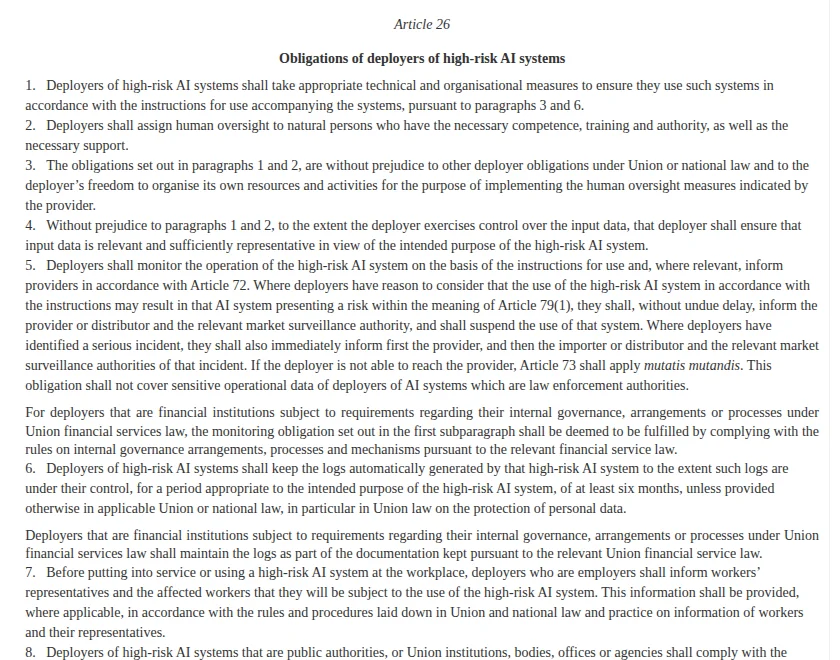
Screenshot: Regulation (EU) 2024/1689, Article 26, consolidated version of July 27, 2026, EUR-Lex.
Article 9 template: risk management record
Article 9 requires a risk management system that is "established, implemented, documented and maintained" and runs as a continuous process across the lifecycle: identify and analyse known and foreseeable risks, estimate and evaluate them, and adopt measures. That's the provider's system. A deployer keeps a shorter record of the risks in its own use, which is what it monitors under Article 26(5) and the starting point for a fundamental rights impact assessment where Article 27 applies.
Copy-paste template:
AI System Risk Management Record
System name: [e.g., "Candidate screening AI, powered by [Vendor]"] Date of assessment: [Date] System owner: [Name, role] Deployment context: [e.g., "Used to score job applications for software engineering roles before human reviewer screen"]
Identified risks:
| Risk | Likelihood (1-5) | Impact (1-5) | Risk score | Mitigation |
|---|---|---|---|---|
| Discriminatory scoring across protected characteristics | [e.g., 3] | [e.g., 5] | [15] | Quarterly bias audit, human review of all rejected candidates in protected groups |
| Model error rates above acceptable threshold | [e.g., 2] | [e.g., 4] | [8] | Monthly accuracy monitoring against hiring outcome data |
| Data breach exposing candidate personal data | [e.g., 2] | [e.g., 5] | [10] | Vendor DPA, data minimization, annual security review |
| System unavailability causing process delays | [e.g., 3] | [e.g., 2] | [6] | Manual backup process documented |
Residual risk assessment: After mitigations, overall residual risk is assessed as [acceptable / requiring escalation] because [brief rationale].
Review schedule: This record will be reviewed [quarterly / annually] and upon any material change to the AI system or deployment context.
Article 10 template: data you control
Article 10 governs the provider's training, validation and testing data. As a deployer, you ask the provider for the information, and you're responsible for the input data you feed in: Article 26(4) says that "to the extent the deployer exercises control over the input data," it must be "relevant and sufficiently representative in view of the intended purpose."
Copy-paste template:
Training Data Record (Deployer)
AI system: [Name and version] Provider: [Company name] Date of information request: [Date] Information received: [Yes / No / Partial]
Provider-supplied training data information:
- Data sources: [e.g., "Provider states training data includes publicly available job postings, proprietary labeled datasets, and synthetic data. Details available in vendor's Annex IV documentation, attached."]
- Data governance practices: [e.g., "Provider confirms data quality checks, de-duplication, and bias testing as described in technical documentation dated [date]."]
- Protected characteristics handling: [e.g., "Provider states model was trained with demographic parity constraints across gender and age."]
Gaps and follow-up: [Note any information the provider has not supplied and what steps you are taking to obtain it. If provider refuses to provide training data information, document this and your risk-based response.]
Article 11 template: technical documentation (Annex IV)
Article 11 requires the provider to draw up Annex IV technical documentation before the system goes on the market, and Article 18 makes it keep that documentation for 10 years. You don't write it; you get it and keep it with your records.

Image: Unsplash.
Copy-paste template:
Technical Documentation Receipt Record
AI system: [Name and version] Provider: [Company name] Documentation version: [e.g., "v2.1, dated [date]"] Document reference: [File name or location]
Confirmation checklist (Annex IV items):
- General description of the AI system and its intended purpose
- Description of design and development process
- Information about training, validation, and testing data
- Description of system monitoring and logging
- Information about accuracy metrics and performance benchmarks
- Cybersecurity measures
Items not covered by provider documentation: [List any gaps. If significant gaps exist, consider whether the system should be deployed without this information.]
Next review date: [Align with provider's documentation update cycle or at least annually]
Article 12 template: logging and record-keeping
Article 12 says high-risk systems "shall technically allow for the automatic recording of events (logs) over the lifetime of the system." The provider builds that in. Your duty is Article 26(6): keep the logs that are under your control "of at least six months," unless other EU or national law, including data protection law, says otherwise.
Copy-paste template:
AI System Logging and Record-Keeping Policy
System: [Name] Log storage location: [e.g., "Vendor-maintained logs accessible via API / Internal data warehouse / Both"] Log retention period: [At least six months (Article 26(6)), longer if other EU or national law requires it]
What is logged:
- Each use of the system: [Yes / No / Partial]
- Input data: [Yes / No. Note: logging input data may create additional data protection obligations]
- Output and recommendation produced: [Yes / No]
- Whether human review was completed: [Yes / No]
- Human override decisions: [Yes / No]
- Timestamp and user ID: [Yes / No]
Access controls: Logs are accessible to [roles with access]. Access is [logged / not logged]. Unauthorized access controls: [describe].
Retention and deletion: Logs under our control are retained for [period, not less than six months] and deleted [automatically / manually] in accordance with [policy reference and GDPR retention schedule].
Article 13 template: instructions for use and notices
Article 13 requires the provider to make the system transparent enough for deployers "to interpret a system's output and use it appropriately," with instructions for use. You follow those instructions (Article 26(1)) and use them for any GDPR data protection impact assessment (Article 26(9)). The notice below covers your separate duty to tell affected people (Article 26(11)). It also reflects their right to an explanation of decisions with legal or similarly significant effects (Article 86) and, for decisions made solely by automated means, the GDPR right "to obtain human intervention" (Article 22).
Copy-paste template (notice to affected people):
Notice of AI-assisted decision-making
[Organisation name] uses an AI system to [describe function, e.g., "assess job applications as part of our recruitment process"].
What the AI system does: [Brief plain-language description, e.g., "The system analyzes application materials to produce a relevance score that our recruitment team uses as one input when selecting candidates for interview."]
Who makes the final decision: A human recruiter reviews AI recommendations before any decision affecting your application is made.
Your rights: If a decision based on this system's output has legal or similarly significant effects on you, you can ask us for a clear explanation of the role the AI system played and the main elements of the decision. Where a decision is made solely by automated means, you can also ask for a person to review it, give your point of view and contest it. Contact [email / process].
Data used: [Description of what data the AI system processes. Align with UK/EU GDPR privacy notice.]
How to get more information: [Contact details]
Article 14 template: human oversight
Article 14 requires the provider to design the system so people can effectively oversee it. Article 26(2) then requires you to "assign human oversight to natural persons who have the necessary competence, training and authority, as well as the necessary support." The plan below records who, how, and when they step in.
Copy-paste template:
Human Oversight Plan
AI system: [Name] Oversight owner: [Role] Date: [Date]
Oversight mechanism:
Outputs from this AI system are reviewed by [role] before any [decision/action] is taken. The AI system [can / cannot] take autonomous action without human review.
Escalation triggers: Human review is mandatory before action when:
- AI system confidence score is below [threshold]
- The decision affects an individual in a [protected category, high-stakes situation]
- The AI system flags an anomaly or uncertainty
- The case is outside the system's documented intended use
Override process: Any human reviewer may override the AI system's recommendation. Overrides are [logged with reason / not logged]. Override rate is reviewed [quarterly] to identify systematic issues.
Training for oversight staff: Staff conducting oversight of this AI system have completed [training, e.g., "AI system user training, date"] and understand [key risk areas].
Stopping the system: The system can be [paused / disabled] by [role] in the event of suspected malfunction or unexpected behaviour. Contact: [name, contact details].
Article 15 template: accuracy, robustness and cybersecurity
Article 15 makes the provider design the system for an appropriate level of accuracy, robustness and cybersecurity and declare the accuracy metrics in the instructions for use. Your part is to monitor against those declared figures and, if use in line with the instructions may present a risk, inform the provider and the market surveillance authority and suspend use (Article 26(5)).
Copy-paste template:
Performance and Robustness Monitoring Record
System: [Name] Monitoring owner: [Role] Monitoring frequency: [Monthly / Quarterly]
Accuracy metrics:
| Metric | Baseline (from vendor documentation) | Current measurement | Date measured | Action if threshold breached |
|---|---|---|---|---|
| [e.g., Precision] | [from vendor docs] | [Current value] | [Date] | Suspend use and contact vendor |
| [e.g., Recall] | [from vendor docs] | [Current value] | [Date] | Suspend use and contact vendor |
| [e.g., False positive rate] | [from vendor docs] | [Current value] | [Date] | Flag for human review |
Robustness checks:
- Out-of-distribution input handling: [How does the system behave when inputs fall outside its training distribution? Describe the check and results.]
- Performance across demographic groups: [Are accuracy metrics consistent across relevant groups? Describe the check and results.]
Cybersecurity: [Describe security measures protecting the AI system, including access controls, data encryption, and vendor security certifications. Reference vendor security documentation.]
Last formal review date: [Date] Next review date: [Date]
Minimum viable documentation checklist
Start with the records that map to deployer duties:
- Human oversight plan with named people and their training (Article 26(2), template above)
- Provider's instructions for use and Annex IV documentation on file (Articles 11, 13, 26(1))
- Log retention set to at least six months for logs under your control (Article 26(6))
- Notice to workers' representatives and affected workers, or to affected people, sent before use (Article 26(7) and (11))
- Risk and monitoring record (Article 9 template, used for Article 26(5) monitoring)
- Fundamental rights impact assessment, if you're a public body, provide public services, or use AI for credit scoring or life and health insurance pricing (Article 27)
For gaps in your current evidence, our EU AI Act deployer evidence gaps guide maps the most common missing items.
Correction (October 19, 2026): Earlier versions said GPAI documentation was due by August 2, 2026. GPAI provider obligations have applied since August 2, 2025, with until August 2, 2027 for models placed on the market before that date (consolidated AI Act, Articles 111 and 113).
Correction (October 20, 2026): Earlier versions said any company that "deploys or develops" an Annex III system must maintain Articles 9-15 documentation, that deployers must produce their own Article 9 risk management documentation, and that documentation must be kept for 10 years under Article 18. Articles 9-15 are requirements the provider must meet (Article 16), and Article 18's 10-year retention applies to providers; a deployer's duties are in Article 26, including keeping logs for at least six months. The sample notice said people have a right to request human review of any AI-assisted decision; the AI Act gives a right to an explanation (Article 86), and GDPR Article 22 gives a right to human intervention only for solely automated decisions. We also removed an out-of-date "months of runway" figure, an unsupported "2-4 hours" completion estimate, and checked-by-default boxes in the Annex IV checklist, and added the Annex I date (August 2, 2028), the two prohibitions that apply from December 2, 2026, and the Article 26(7), 26(11) and Article 27 duties.
Related reading
- EU AI Act deployer evidence gaps SME August 2026
- EU AI Act compliance guide for small teams
- EU AI Act August 2026 what is delayed vs what applies
- EU AI Act GPAI compliance checklist August 2
- EU AI Act Annex III high-risk AI systems
- AI governance checklist 2026
- ISO 42001 vs NIST AI RMF for small teams
- AI tool register template for small teams
- Third-party AI tool risk assessment template
- One documentation set for EU AI Act, NIST AI RMF, and Texas TRAIGA
- AI Model Cards in 2026: What Regulators Now Expect and How to Write One
- EU AI Act Conformity Assessment: What It Is and Who Must Do It
- AI risk register template with likelihood x impact scoring
Sources: Regulation (EU) 2024/1689, consolidated text of July 27, 2026 (EUR-Lex), European Commission, AI Omnibus enters into force, GDPR Article 22.
