
Image: Pexels, used under the Pexels License.
Start with the NIST AI RMF. It's a free framework that tells you what good AI risk management looks like, and you can work through it yourself. ISO 42001 is a standard you get audited against, and the certificate is the point: buy into it when someone you sell to asks for one. Until then, it's paperwork for an audience you don't have yet.
The two side by side
| ISO/IEC 42001 | NIST AI RMF | |
|---|---|---|
| What it is | International standard for an AI management system | Framework for managing AI risk |
| Published by | ISO and IEC (committee JTC 1/SC 42) | US National Institute of Standards and Technology |
| Date | December 2023, edition 1 | January 26, 2023 (version 1.0, now being revised) |
| How you use it | Build the management system, then a certification body audits it | Voluntary; you apply it yourself |
| What you get | A certificate a customer can check | Your own documented practice, no certificate |
| Cost to get the text | CHF 225 | Free download, with a free Playbook |
| Structure | Management system clauses, like other ISO management standards | Four functions: Govern, Map, Measure, Manage |
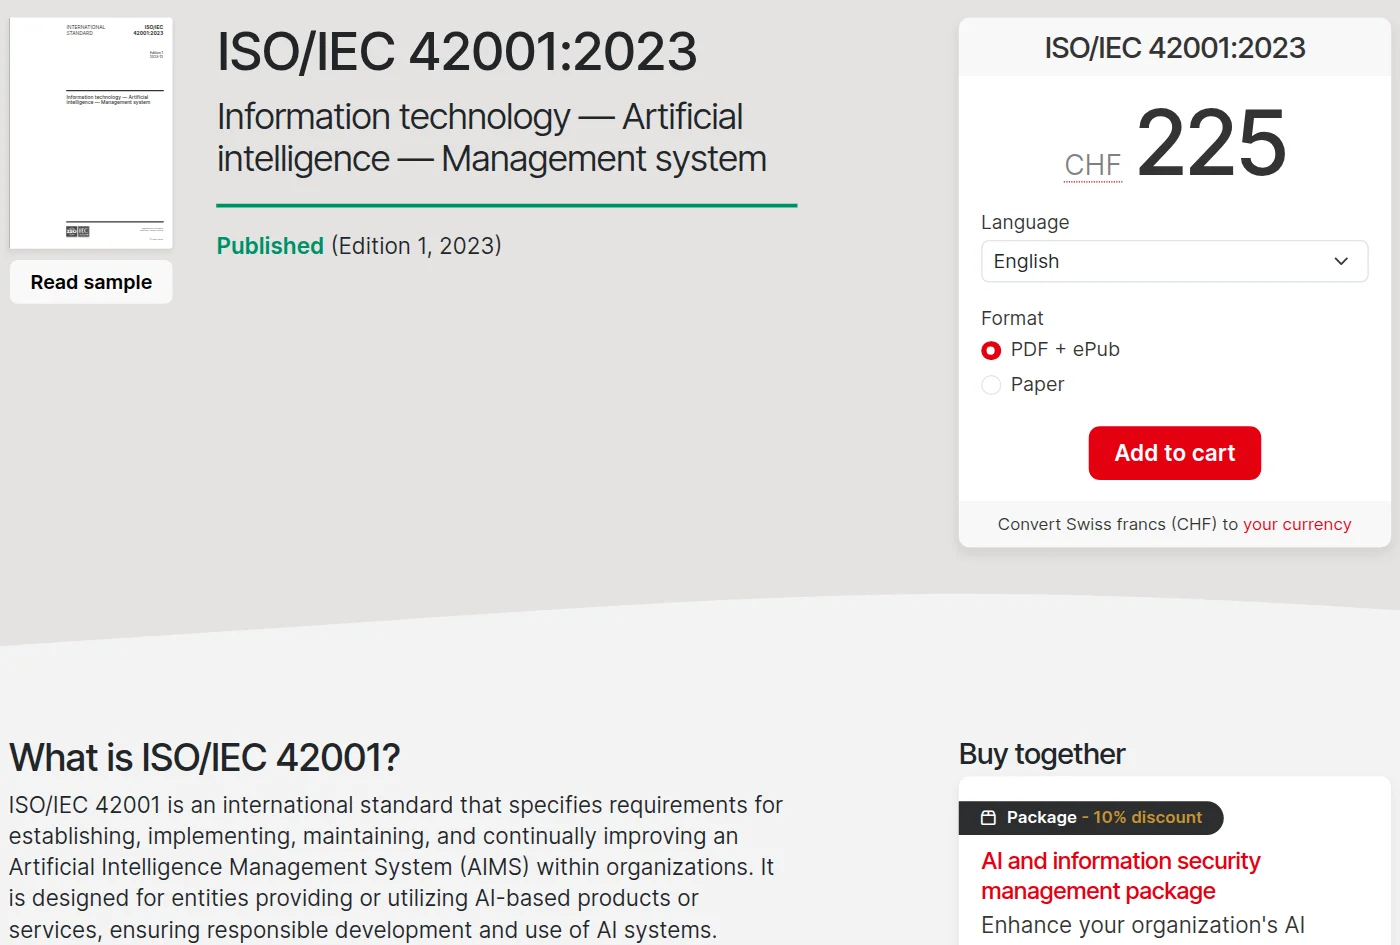
Screenshot: ISO, "ISO/IEC 42001:2023", captured October 15, 2026.
What ISO 42001 asks of you
ISO describes 42001 as a standard that "specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS)." In practice that means a written AI policy, objectives, a process for assessing AI risk, internal audits and management review, run as an ongoing system rather than a one-off document.
The output that matters commercially is the certificate. Certification bodies audit you against 42001, and since July 2025 a companion standard, ISO/IEC 42006, sets the requirements those bodies have to meet. When a buyer asks "are you ISO 42001 certified?", check that the body that issued your certificate works to it.
Who needs it: teams selling AI products or AI-heavy services to enterprises or public bodies whose vendor questionnaires or tenders ask for the certificate by name. If you already run ISO 27001, 42001 follows the same management-system pattern, so the second audit builds on habits you have.
Be clear about what the certificate proves. On r/cybersecurity, a poster who had just taken their employer through ISO 42001 called the result "kinda underwhelming", and the top reply put the limit plainly: "ISO has too much focus on policy documentation and not enough specific testing," wrote Affectionate-Panic-1. Another reader going through it said it "will be cool on a sticker for the marketing department," wrote irishcybercolab. That's the trade: a certificate buyers recognize, not proof your models behave.
https://www.reddit.com/r/cybersecurity/comments/1ow1m6k/got_my_employer_iso_42001_certified_and_became_an/
What the NIST AI RMF asks of you
NIST says the AI RMF "is intended for voluntary use." It organizes the work into four functions:
| Function | What it covers |
|---|---|
| Govern | Policies, roles and accountability for AI risk |
| Map | The context, risks and impacts of each AI system |
| Measure | Testing and tracking those risks |
| Manage | Prioritizing and acting on them over time |
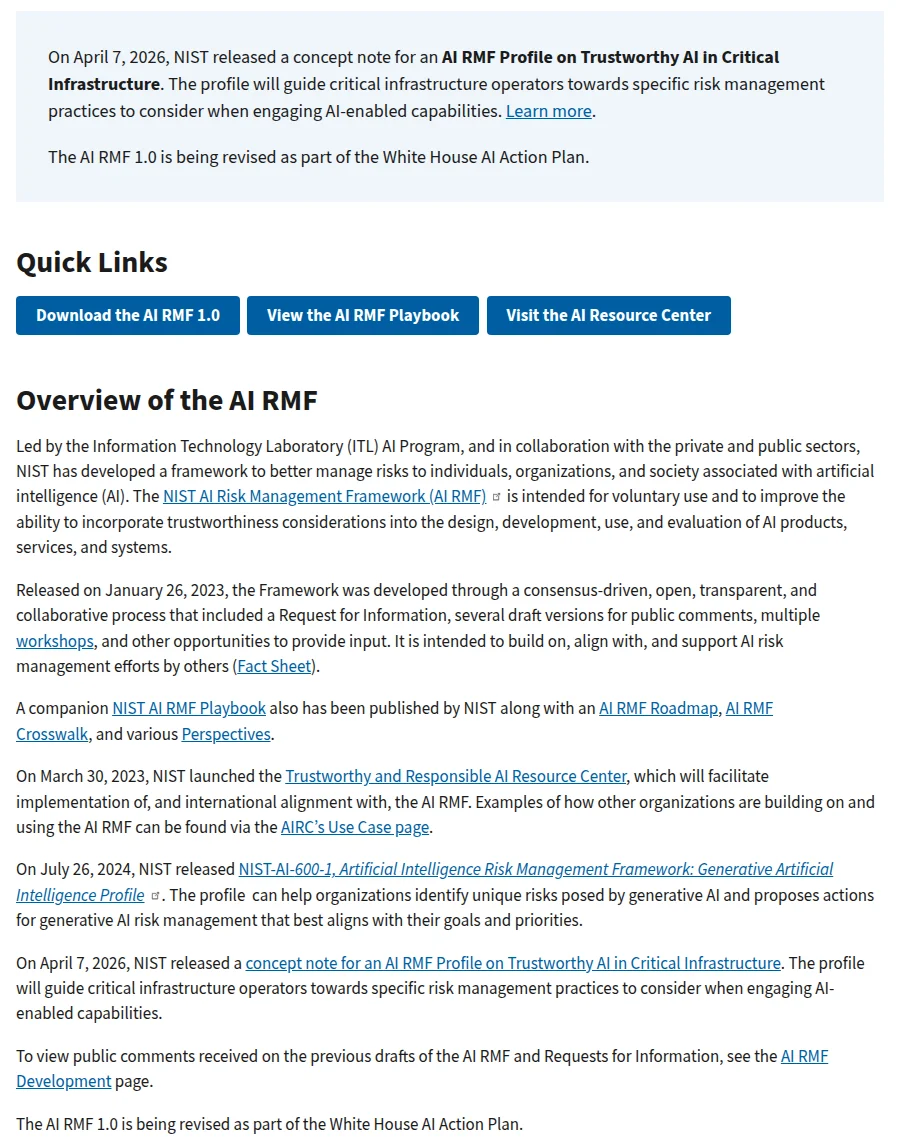
Screenshot: NIST, "AI Risk Management Framework", captured October 15, 2026.
The companion Playbook lists suggested actions for each subcategory. NIST is clear it's "neither a checklist nor set of steps to be followed in its entirety": you borrow what fits. For generative AI there's a separate profile, NIST-AI-600-1, released July 26, 2024.
One thing to plan around: the framework is mid-revision. NIST's page says "The AI RMF 1.0 is being revised as part of the White House AI Action Plan," and the Playbook will be updated after that.
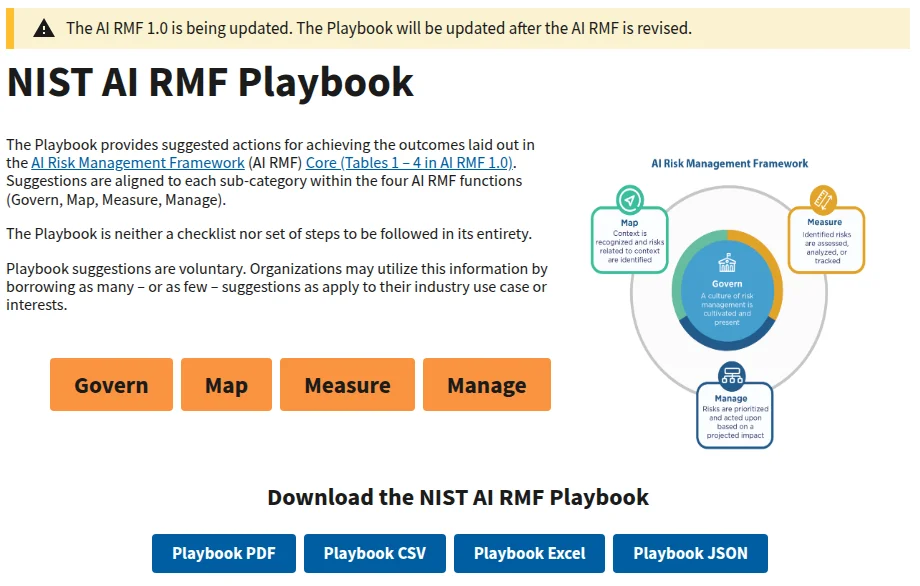
Screenshot: NIST AI Resource Center, "NIST AI RMF Playbook", captured October 15, 2026.
That's not a reason to wait. The four functions aren't going anywhere, and the work you do now (an inventory of AI systems, an owner for each, a risk review before launch) is the same work any revision will ask for.
Texas TRAIGA: where both frameworks count
Texas's Responsible AI Governance Act (HB 149) took effect January 1, 2026. It doesn't give NIST users a blanket safe harbor. Section 552.105 says a defendant in an attorney general action can't be found liable if it discovers the violation through, among other routes, an internal review process while it "substantially complies with the most recent version of the 'Artificial Intelligence Risk Management Framework: Generative Artificial Intelligence Profile'" from NIST "or another nationally or internationally recognized risk management framework for artificial intelligence systems."
Two things follow. The text names NIST's Generative AI Profile, not just the core framework. And the law leaves room for other frameworks: ISO 42001 is an international AI management standard, so it's a strong candidate, though the text doesn't name it. The bill text also gives everyone a rebuttable presumption of reasonable care. For the details, see our Texas TRAIGA and NIST AI RMF checklist.
The EU AI Act: neither one is enough
For high-risk AI systems, the AI Act asks for several separate things: a risk management system (Article 9), a quality management system from providers (Article 17), technical documentation (Article 11), human oversight (Article 14) and a conformity assessment (Article 43). An ISO 42001 management system and NIST-style risk reviews give you a head start on Articles 9 and 17, but neither is the conformity assessment.
The shortcut the Act does offer is Article 40: systems that conform to harmonised standards "the references of which have been published in the Official Journal" are presumed to meet the requirements. Before treating any certificate as proof of AI Act compliance, check whether that standard is on the list. For the full picture, see the EU AI Act guide for small teams.
What each costs
ISO 42001. The standard costs CHF 225 from ISO's store. The real cost is the certification audit and the time to build the management system first. Certification bodies quote by scope, sites and headcount, and we couldn't find a published price list from one, so we won't print a range. Ask two or three accredited bodies for written quotes covering the initial audit and the yearly follow-up audits.
NIST AI RMF. The framework, the Playbook and the Generative AI Profile are free downloads. The cost is your team's time, plus a consultant if you want one.
Which to choose
Go with the NIST AI RMF if:
- No customer has asked you for a certificate yet
- You're building AI governance for the first time
- You sell in the US and want to line up with frameworks Texas law already names
Go for ISO 42001 certification if:
- A customer questionnaire, contract or tender asks for it by name
- You already hold ISO 27001 and can extend the same management system
- Your buyers are mostly outside the US and expect ISO certificates from suppliers
Or both, in order. Run NIST now: build the inventory, assign owners, set a risk review. When a deal needs the certificate, move that material into an ISO 42001 management system. The work carries over; only the audit is new.
What neither framework does for you
Neither one tells you which of your AI tools is high-risk, which vendor terms to accept, or what to write in a staff policy. You still need:
- An AI tool register listing what you use and who owns it
- Vendor due diligence for each AI provider
- Named roles for approving and reviewing AI use
Correction, October 15, 2026: an earlier version said EU AI Act Article 9 requires a quality management system and conformity assessment; Article 9 covers the risk management system, Article 17 the quality management system and Article 43 conformity assessment. It said Texas TRAIGA's safe harbor references the NIST AI RMF directly; the law names NIST's Generative AI Profile or another recognized framework, which leaves room for ISO 42001, and it's a defense tied to an internal review, not a blanket safe harbor. It cited FTC guidance and US executive orders as referencing the NIST AI RMF without a source, and gave certification cost ranges we couldn't source; we removed them. It also listed ISO 42001 clause requirements we couldn't check against the paywalled text; we removed that table.
