
Image: Unsplash.
Updated October 17, 2026: every legal statement below was checked against the consolidated text of the AI Act (version of July 27, 2026) and the Digital Omnibus in the Official Journal. The correction note is at the end. How the extension happened →
If your team uses someone else's AI system at work, the EU AI Act treats you as a deployer. For deployers, a few duties already apply, and the big one is more than a year away. The high-risk rules for AI used in hiring, credit scoring, education and the other Annex III areas apply from December 2, 2027. The Digital Omnibus on AI, Regulation (EU) 2026/1744, moved them back from August 2, 2026.
What applies today is short: the Article 5 bans, an AI literacy duty that the Omnibus softened, and the Article 50 transparency rules for chatbots, generated content and deepfakes. The obligations for general-purpose AI (GPAI) models sit with the companies that train them, not with the teams that call their APIs.
This guide walks through the order we'd do it in: role, bans, classification, deployer duties, vendor file, literacy, transparency. The checklist at the end is copy-paste.
Where the deadlines stand
| Date | What applies | Who it hits |
|---|---|---|
| February 2, 2025 | Chapters I and II: the Article 5 bans and the Article 4 AI literacy duty | Providers and deployers |
| August 2, 2025 | GPAI model obligations (Chapter V) and the penalty rules (Chapter XII) | Model providers; Member States |
| August 2, 2026 | General date of application, including Article 50 transparency and the Commission's power to fine GPAI providers (Article 101) | Providers and deployers |
| December 2, 2026 | Two new bans (non-consensual intimate imagery, child sexual abuse material); Article 50(2) marking for generators already on the market | Providers of generative AI; deployers who use a system to produce that material |
| August 2, 2027 | GPAI models placed on the market before August 2, 2025 must comply | Model providers |
| December 2, 2027 | High-risk rules for Annex III systems (Chapter III, Sections 1 to 3) | Providers and deployers |
| August 2, 2028 | High-risk rules for AI in Annex I products such as medical devices, toys and lifts | Product makers |
| August 2, 2030 | High-risk systems already on the market that public authorities use | Public-sector providers and deployers |
The Omnibus was dated July 8, 2026, published in the Official Journal on July 24 and entered into force three days later, on July 27. The European Parliament adopted its position on June 16 and the Council its decision on June 29. Before the Omnibus, the Annex I date was August 2, 2027.
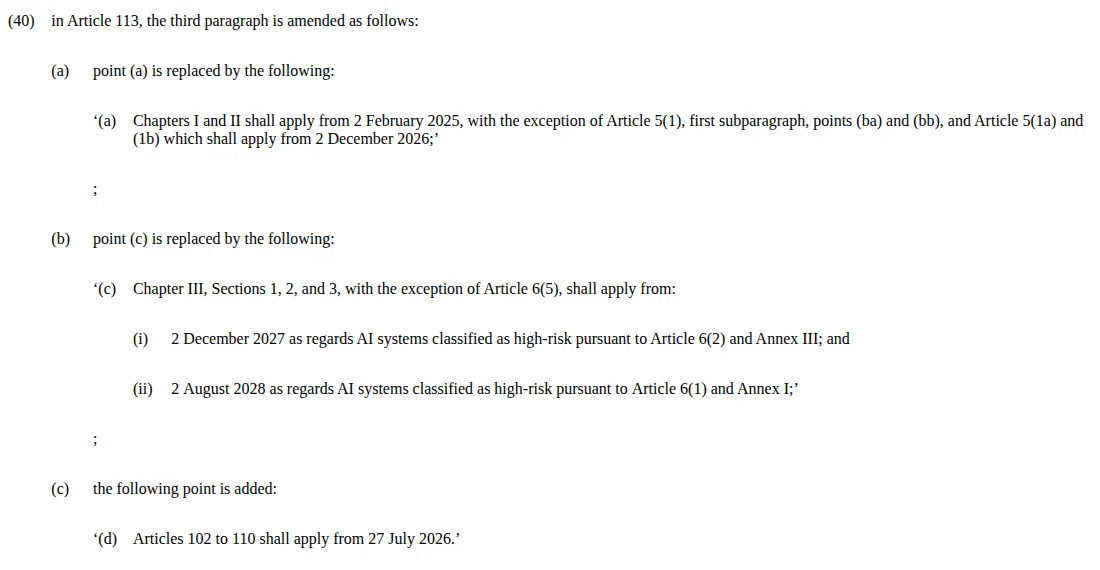
Screenshot: Regulation (EU) 2026/1744, point (40), amending Article 113. Source: EUR-Lex, Publications Office of the European Union.
One transitional rule matters if you already run a high-risk tool. Under Article 111(2) as amended, a high-risk system placed on the market or put into service before the Chapter III date is covered only if its design changes significantly from that date. Public-authority systems get no such pass: they must comply by August 2, 2030.
Video: euronews, "Lawmakers approve AI Act with overwhelming majority" (March 13, 2024, the Parliament's vote on the original Act).
Step 1: Work out whether you are a provider or a deployer
The Act splits duties by role, so this comes first.
- Provider (Article 3(3)): develops an AI system or GPAI model, or has one developed, and places it on the market or puts it into service under its own name or trademark, paid or free.
- Deployer (Article 3(4)): uses an AI system under its authority, except in a personal, non-professional activity.
Where you are based matters less than where the output lands. Article 2(1) covers providers placing AI on the EU market wherever they are established, deployers established or located in the EU, and providers and deployers in a third country "where the output produced by the AI system is used in the Union."
A deployer can turn into a provider. Article 25(1) treats you as the provider of a high-risk system if you put your name or trademark on one, make a substantial modification to one, or change the intended purpose of a system that wasn't high-risk, a general-purpose system included, so that it becomes high-risk. In our reading, the common small-team version is wiring a general chatbot into CV screening: Annex III lists AI used "to analyse and filter job applications."
Step 2: Rule out the banned uses
Article 5 has applied since February 2, 2025. No documentation makes these lawful. The list, shortened:
- (a) subliminal, manipulative or deceptive techniques that materially distort behaviour and cause, or are reasonably likely to cause, significant harm
- (b) exploiting vulnerabilities due to age, disability or a specific social or economic situation
- (c) social scoring by anyone, public or private, that leads to unjustified or out-of-context detrimental treatment
- (d) predicting that a person will commit a crime based solely on profiling or personality traits
- (e) building facial recognition databases through untargeted scraping of facial images from the internet or CCTV footage
- (f) inferring emotions of a person at the workplace or in education, except for medical or safety reasons
- (g) biometric categorisation to infer race, political opinions, trade union membership, religious or philosophical beliefs, sex life or sexual orientation
- (h) real-time remote biometric identification in publicly accessible spaces for law enforcement, with narrow exceptions
From December 2, 2026, two more apply: AI that generates or manipulates realistic intimate or sexually explicit images, video or audio of an identifiable person without explicit consent, and AI that generates child sexual abuse material. For a system on sale, the ban bites when that output is its intended purpose or a foreseeable, reproducible result without adequate safeguards. A deployer breaks it by using a system for the purpose of producing that material.
For the team-level read, point (f) is the one to check. Mood or engagement scoring of staff from faces, voice or other biometric signals falls under it. The Article 5 guide covers the exceptions.
Step 3: Classify each tool
A system is high-risk by one of two routes.
Annex I (Article 6(1)): the AI is a safety component of a product, or is itself a product, covered by the EU product laws in Annex I, and that product needs a third-party conformity assessment. The list includes medical devices (Regulation (EU) 2017/745) and in vitro diagnostics (2017/746). This route applies from the 2028 date.
Annex III (Article 6(2)): the AI is used in one of eight areas.
| Annex III area | What the text lists |
|---|---|
| 1. Biometrics | Remote biometric identification (not one-to-one verification), biometric categorisation by sensitive attributes, emotion recognition |
| 2. Critical infrastructure | Safety components in managing critical digital infrastructure, road traffic, or the supply of water, gas, heating or electricity |
| 3. Education | Admission, evaluating learning outcomes, assessing the level of education a person gets, monitoring students during tests |
| 4. Employment | Recruitment and selection (targeted job ads, filtering applications, evaluating candidates); decisions on promotion, termination, task allocation; monitoring performance and behaviour |
| 5. Essential services | Public benefit eligibility; creditworthiness and credit scores (fraud detection excluded); risk assessment and pricing for life and health insurance; emergency call triage |
| 6. Law enforcement | Victim risk, polygraphs, evidence reliability, re-offending risk, profiling |
| 7. Migration and border | Polygraphs, risk assessment, asylum and visa examination, identification |
| 8. Justice and democracy | Assisting courts in researching and applying the law; influencing elections |
Two details in that table catch teams out. Insurance is in scope only for life and health cover. And healthcare AI is mostly an Annex I question: clinical tools are high-risk through the medical device rules, not through Annex III.
The Article 6(3) exit. An Annex III system is not high-risk where it "does not pose a significant risk of harm" and meets one of four conditions: it performs a narrow procedural task, improves the result of a completed human activity, detects patterns without replacing human assessment, or does a preparatory task. There is no exit for profiling: an Annex III system "shall always be considered to be high-risk where the AI system performs profiling of natural persons." A provider relying on the exit must document its assessment before sale (Article 6(4)) and register the system in the EU database (Article 49(2)).
Write the reasoning down even as a deployer. A reply in r/gdpr put it plainly: "I have seen orgs with immaculate test logs still struggle in conformity assessment cause no one had documented why the system was classified high risk in the first place." Another commenter in that thread summed up the whole Act as "a risk based safety product law."
https://www.reddit.com/r/gdpr/comments/1wqd9fa/the_eu_ai_act_doesnt_ask_if_its_safe_it_asks_if/pc398zz/
The Annex III yes/no checklist turns this step into questions per tool.
Step 4: What deployers of a high-risk system must do
These duties start on the Annex III date. Article 26 is the list:
- Use the system in line with the provider's instructions for use (26(1)).
- Assign human oversight to people "who have the necessary competence, training and authority" (26(2)).
- Where you control the input data, keep it relevant and sufficiently representative for the intended purpose (26(4)).
- Monitor the system. If you think it presents a risk, inform the provider or distributor and the market surveillance authority and suspend use. If you identify a serious incident, inform the provider first, then the importer or distributor and the authorities (26(5)).
- Keep the logs under your control for at least six months, unless other law says otherwise (26(6)).
- As an employer, inform workers' representatives and the affected workers before using a high-risk system at the workplace (26(7)).
- Where you decide about people, or help decide, with an Annex III system, tell them they are subject to it (26(11)).
- Use the provider's Article 13 information for your GDPR data protection impact assessment, where one applies (26(9)).
Two more duties sit outside Article 26. Under Article 86, a person affected by a decision based on an Annex III system that has legal or similarly significant effects can ask you for "clear and meaningful explanations of the role of the AI system in the decision-making procedure and the main elements of the decision taken." And Article 27 requires a fundamental rights impact assessment from public bodies, private entities providing public services, and any deployer using AI for credit scoring or life and health insurance pricing. Since the Omnibus, that assessment can cross-refer to your existing DPIA.
What human oversight means in the text. Article 14(4) says the people assigned must be able to understand the system's capacities and limitations, stay aware of automation bias, interpret the output correctly, decide not to use it or override it, and stop it with a "stop" button or similar procedure. The provider has to build those capabilities in; you have to staff them. More in what Article 14 requires.
Step 5: What your vendor must have, and what to ask for
Article 16 puts the heavy lifting on the provider. Before sale, a provider of a high-risk system must:
- meet the Section 2 requirements (risk management, data governance, technical documentation per Annex IV, logging, transparency, human oversight, accuracy and cybersecurity)
- run a quality management system (Article 17)
- complete the conformity assessment (Article 43)
- sign an EU declaration of conformity (Article 47) and affix the CE marking (Article 48)
- register itself and the system in the EU database (Article 49(1))
After sale it runs post-market monitoring (Article 72) and reports serious incidents to the market surveillance authority no later than 15 days after becoming aware, 2 days for a widespread infringement or a serious and irreversible disruption of critical infrastructure, and 10 days where a person died (Article 73).
The Omnibus gave smaller providers some relief. SMEs, start-ups and small mid-caps (SMCs) may provide the Annex IV technical documentation "in a simplified manner," on a form the Commission will publish, and their quality management system can be proportionate to their size.
What the text does not say. Article 26 doesn't tell a private deployer to collect the declaration of conformity. Only public-authority deployers are told not to use a system missing from the EU database (26(8)). In our view you should ask for it anyway: a vendor that can't produce it hasn't done its part, and you are the one facing the affected person.
Questions to send in writing, per high-risk tool:
- Is this system high-risk under Annex III or Annex I? If you rely on the Article 6(3) exit, send the assessment.
- Send the EU declaration of conformity and the EU database registration entry.
- Send the instructions for use, including known limitations and the human oversight measures you built in.
- What logs does the system generate, and which of them are under our control?
- How will you inform us of serious incidents and corrective actions?
- What can we tell a person who asks how the AI was used in their decision?
The AI vendor due diligence checklist has the wider review, and the Annex IV guide lists what the technical file contains.
AI literacy: what Article 4 asks now
The original Article 4 told providers and deployers to take measures to ensure, "to their best extent, a sufficient level of AI literacy" of their staff. The Omnibus replaced it. Providers and deployers must now "take measures to support the development of AI literacy" of their staff and others operating AI on their behalf, and the duty "does not require providers or deployers to guarantee any specific level of AI literacy of any individual." The Commission is to publish practical examples.
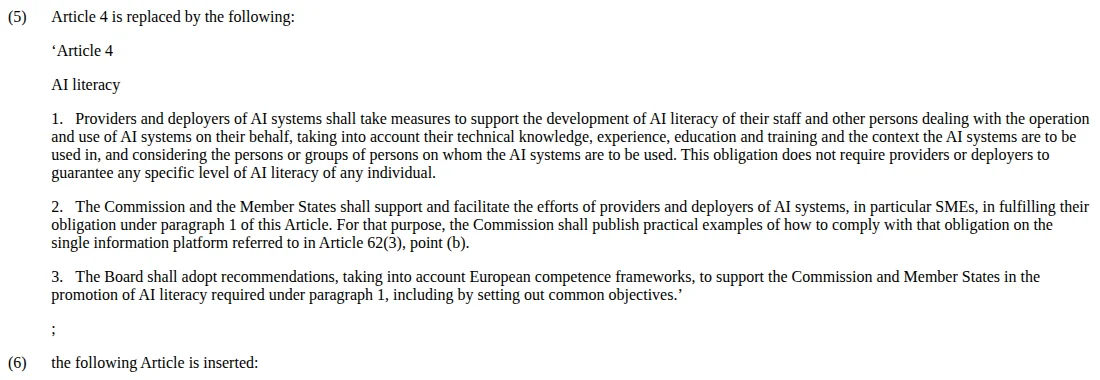
Screenshot: Regulation (EU) 2026/1744, point (5), the new Article 4. Source: EUR-Lex, Publications Office of the European Union.
For a small team that means a short, documented training and an acceptable-use policy that names who may use which tool for what. It doesn't mean a certification programme.
Transparency duties under Article 50
These apply to everyone, high-risk or not, and have applied since August 2, 2026:
- Chatbots (50(1), providers): people must be told they are interacting with an AI system, unless that is obvious.
- Generated content (50(2), providers): synthetic audio, image, video or text must be marked in a machine-readable format and be detectable. Generators already on the market before August 2, 2026 have until December 2, 2026.
- Emotion recognition and biometric categorisation (50(3), deployers): inform the people exposed.
- Deepfakes (50(4), deployers): disclose that image, audio or video content was artificially generated or manipulated.
- Public-interest text (50(4), deployers): disclose AI-generated text published to inform the public, unless it went through human review or editorial control and someone holds editorial responsibility.
The information must reach people "at the latest at the time of the first interaction or exposure" (50(5)).
If you build on GPT, Claude or Gemini
GPAI model providers must, under Article 53(1), keep technical documentation of the model, give downstream providers the information they need to integrate it, put in place a copyright policy, and publish a summary of the content used for training. A model is presumed to carry systemic risk, with extra duties, when its training compute is greater than 10^25 floating point operations (Article 51(2)). The Commission published the GPAI Code of Practice on July 10, 2025, in three chapters: Transparency, Copyright, and Safety and Security.
None of that is yours if you only call an API. What can become yours is the system you build on top: under Article 25(1)(c), repurposing a general-purpose system for an Annex III use makes you the provider of a high-risk system. The GPAI checklist covers the model-provider side.
Penalties
| Infringement | Maximum fine |
|---|---|
| Prohibited practices (Article 99(3)) | EUR 35 million or 7% of worldwide annual turnover |
| Most other obligations (Article 99(4)) | EUR 15 million or 3% |
| Incorrect or misleading information to authorities (Article 99(5)) | EUR 7.5 million or 1% |
The higher of the two applies to large companies. For SMEs and start-ups, each cap is whichever is lower (Article 99(6)); the Omnibus extended that to SMCs for the 99(4) and 99(5) fines, and told Member States to take the interests and economic viability of SMEs and SMCs into account.
GDPR keeps running alongside. Article 2(7) says the Act "shall not affect" Regulation (EU) 2016/679, so a high-risk tool that processes personal data needs both files.
EU AI Act compliance checklist
Now
- List every AI tool in use, including AI features inside SaaS products, and who owns each one
- For each tool, record whether you are provider or deployer (Article 3), and whether any output is used in the EU
- Confirm no tool falls under Article 5; check emotion inference on staff or students specifically
- Take documented AI literacy measures: short training, an acceptable-use policy, named owners (Article 4)
- If you ship a chatbot or generator, check the Article 50 notices and machine-readable marking
Before December 2, 2027
- Classify each tool against Annex III and Annex I; write down the reasoning, including any Article 6(3) exit
- Flag any plan to repurpose a general-purpose tool for an Annex III use (Article 25)
- Send the six vendor questions above and keep the answers
- Name trained people for human oversight and give them the authority to override and stop the system
- Set up log retention of at least six months for the logs you control
- Draft the Article 26(11) notice, the worker information under 26(7), and a process for Article 86 explanation requests
- If you score credit or price life or health insurance, plan the Article 27 impact assessment alongside your DPIA
- Agree with each vendor how serious incidents are reported to you, and how you report them back
Correction (October 17, 2026): A full check against the consolidated text found further errors, now fixed. The Annex III table listed "real-time" remote biometric identification (Annex III covers remote biometric identification generally, excluding verification), all insurance risk (only life and health insurance), and critical infrastructure management (only safety components). It placed clinical AI under Annex III (medical device AI is high-risk through Annex I, from August 2, 2028). It said a deployer "cannot deploy" a system without the vendor's declaration of conformity and that registration is a prerequisite for every deployer (Article 26 has no such rule for private deployers; public-authority deployers must not use unregistered systems). It described human oversight as access to "model reasoning" (Article 14(4) lists understanding, automation-bias awareness, interpretation, override and stop). It said all GPAI providers must publish model evaluation results (Article 53 requires documentation, downstream information, a copyright policy and a public training-content summary), and that candidates can request human review (the Act gives a right to an explanation, Article 86). The scope FAQ said "output affects EU residents" (Article 2(1)(c): output used in the Union). We also added the Article 4 change, the Article 6(3) exit, Articles 25, 27, 73 and 111(2), and the SMC fine rule, and removed the Colorado section and an unsourced framework table.
Correction (October 15, 2026): An earlier version gave July 27 as the Omnibus publication date (published July 24, in force July 27), said GPAI providers had to comply by August 2, 2026 (obligations from August 2, 2025; Commission fines from August 2, 2026), gave June 2, 2026 for the GPAI Code of Practice (published July 10, 2025) and cited Article 99(4) for the incorrect-information fine (Article 99(5)).
Correction (October 19, 2026): A second check against the same texts tightened three statements. The new December 2026 bans also bind deployers who use a system to produce that material (Article 5(1a)), and the first one covers sexually explicit as well as intimate material (Article 5(1), point (ba)). The Article 6(3) exit needs one of its four conditions, not just an example of them. The two-day incident deadline in Article 73(3) also covers a serious and irreversible disruption of critical infrastructure.
Primary texts
- AI Act, consolidated version of July 27, 2026 (EUR-Lex; consolidated texts are a documentation tool, the Official Journal versions are authentic)
- Regulation (EU) 2024/1689, the AI Act, Official Journal, July 12, 2024
- Regulation (EU) 2026/1744, the Digital Omnibus on AI, Official Journal, July 24, 2026
Screenshot: EUR-Lex record for Regulation (EU) 2024/1689, October 2026. Source: EUR-Lex, Publications Office of the European Union.
Related Reading
- EU Digital Omnibus, AI Act deadline extension explained
- What is the EU AI Act, plain-English explainer
- EU AI Act Annex III checklist, is your AI high-risk?
- EU AI Act prohibited AI practices, Article 5
- Human-in-the-loop AI: what Article 14 requires
- EU AI Act Annex IV technical documentation guide
- EU AI Act conformity assessment process
- EU AI Act post-market monitoring, Article 72
- EU AI Act Article 13 transparency for deployers
- EU AI Act Article 9 risk management system
- EU AI Act high-risk classification guidelines
- EU AI Act SME sandbox and support measures
- EU AI Act August 2026: what's delayed and what still applies
- EU AI Act GPAI compliance checklist
- EU AI Act GPAI codes of conduct
- HR AI governance for hiring decisions
- Healthcare AI governance: HIPAA, EU AI Act and FDA
- Fintech AI governance: CFPB, FCRA and EU AI Act
- AI vendor due diligence checklist
- GDPR-compliant AI assistants compared
- ISO 42001, EU AI Act and NIST AI RMF: which framework applies
- AI incident reporting obligations
- GDPR AI fines: enforcement cases small teams must know
- AI governance for small teams: complete guide
