
If your company sends personal data to an AI tool and Article 30 applies to you, that tool needs an entry in your record of processing activities. The entries below cover 12 tools teams use at work. Your half (purpose, data subjects, your retention) you fill in. The vendor half is where copied templates go wrong, so we checked every vendor cell against the vendor's own DPA, terms or privacy page on October 16, 2026.
Image: Pexels, used under the Pexels License.
What Article 30 Requires
Article 30 GDPR requires controllers to maintain a written record (the RoPA) covering every processing activity they carry out. For each activity, the record must include:
| Field | What to document | Required by Art. 30? |
|---|---|---|
| Purpose | Why you are processing the data | Yes |
| Legal basis | Which GDPR legal basis applies (Art. 6 and Art. 9 if special categories) | Not in Art. 30(1); the ICO recommends recording it alongside |
| Categories of data subjects | Who the data belongs to (customers, employees, prospects) | Yes |
| Categories of personal data | What data is processed (names, emails, health data, etc.) | Yes |
| Recipients | Who receives the data, including processors (the AI vendor) | Yes |
| Third-country transfers | Whether data leaves the EEA, which country it goes to, and the safeguard you rely on | Yes (documenting safeguards is required for Art. 49(1) second-subparagraph transfers) |
| Retention period | Time limits for erasure, including what the AI vendor retains | Where possible |
| Security measures | A general description of the Art. 32(1) technical and organisational measures | Where possible |
Note on legal basis: Article 30(1) doesn't list legal basis. The ICO's documentation guidance says it "makes good business sense" to record it alongside, because your privacy notice has to state it anyway. We include it in every entry below.
AI tools add complexity to almost every one of these fields:
- Recipients: the AI vendor is your processor under Article 28 and goes in the recipients field; the model providers it uses are its sub-processors
- Third-country transfers: several of the vendors below process data in the US, so the entry needs the safeguard (SCCs, the EU-US Data Privacy Framework or binding corporate rules)
- Retention: vendor retention runs from "not retained by default" (GitHub Copilot in the IDE) to 30 days (OpenAI and Anthropic APIs) to whatever you configure (Microsoft 365, Salesforce), so copy the vendor's own wording
- Security: point to the vendor's DPA and its audit reports rather than describing their controls yourself

Image: Pexels, used under the Pexels License.
RoPA Template: 12 AI Tools, Pre-Filled
Copy each block into your RoPA document. Adjust fields marked [customize] for your specific use case.
1. ChatGPT API (OpenAI)
| Field | Entry |
|---|---|
| Activity name | AI text generation and analysis, ChatGPT API |
| Controller | [Your company name] |
| DPO (if applicable) | [DPO name and contact, if you have one] |
| Purpose | [customize], e.g., customer support drafting, document summarization, internal query answering |
| Legal basis | Legitimate interests (Art. 6(1)(f)), efficient processing of business queries; or Contract (Art. 6(1)(b)) if used directly for customer service |
| Categories of data subjects | [customize], e.g., customers, employees, end users |
| Categories of personal data | [customize], e.g., names, email addresses, customer query content, document text containing PII |
| Processor | OpenAI OpCo, LLC (1455 3rd Street, San Francisco, CA 94158, USA). If your company is in the EEA or Switzerland, the DPA is with OpenAI Ireland Ltd. |
| Third-country transfer | Yes, US processing unless you use European data residency for eligible API projects. Safeguard: the 2021 SCCs (Modules 2 and 3) or an adequacy decision, per the OpenAI DPA |
| Vendor retention | Abuse monitoring logs kept up to 30 days, unless the law requires longer. Zero Data Retention needs OpenAI's approval |
| Your retention | [customize], e.g., 90 days in your logging system; then deleted |
| Training on data | No. API data hasn't been used for training since March 1, 2023, unless you opt in |
| Security measures | AES-256 at rest, TLS 1.2+ in transit; SOC 2 Type 2 audit of the API platform (OpenAI Trust Portal) |
| DPA reference | OpenAI Data Processing Addendum, effective January 1, 2026, part of the OpenAI Services Agreement |
2. Claude API (Anthropic)
| Field | Entry |
|---|---|
| Activity name | AI text generation and analysis, Claude API |
| Controller | [Your company name] |
| DPO (if applicable) | [DPO name and contact] |
| Purpose | [customize], e.g., document review, code review, customer query answering |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | [customize] |
| Categories of personal data | [customize] |
| Processor | Anthropic Ireland, Limited (6th Floor, South Bank House, Barrow Street, Dublin 4, D04 TR29, Ireland) if your company is in the EEA, Switzerland or UK; otherwise Anthropic, PBC (548 Market St, PMB 90375, San Francisco, CA 94104, USA) |
| Third-country transfer | Yes, US processing (the API's only workspace data location is the US). Safeguard: SCCs, Module Two (controller to processor) or Module Three, in the Anthropic DPA |
| Vendor retention | Inputs and outputs deleted from Anthropic's backend within 30 days, unless you have a Zero Data Retention agreement or the content is held for Usage Policy enforcement |
| Your retention | [customize] |
| Training on data | No, by default for commercial products, the API included |
| Security measures | SOC 2 Type 2, ISO 27001 and ISO 42001 (Anthropic Trust Center) |
| DPA reference | Anthropic Data Processing Addendum, effective February 24, 2025, part of the Commercial Terms |
3. GitHub Copilot (GitHub)
| Field | Entry |
|---|---|
| Activity name | AI code completion, GitHub Copilot |
| Controller | [Your company name] |
| Purpose | Developer productivity, code completion and suggestion |
| Legal basis | Legitimate interests (Art. 6(1)(f)), productivity tool for software development |
| Categories of data subjects | Employees (developers), code they write may incidentally contain PII in comments, variable names, or test data |
| Categories of personal data | Code content (may contain PII if developers embed real data in code); developer account data |
| Processor | GitHub, Inc. (88 Colin P. Kelly Jr. St., San Francisco, CA 94107, USA) |
| Third-country transfer | Yes, US processing. Safeguard: the 2021 SCCs in the GitHub DPA; GitHub is also certified under the Data Privacy Framework. Copilot data residency in the EU needs GitHub Enterprise Cloud with data residency |
| Vendor retention | Business and Enterprise defaults: IDE chat, code completions and Copilot CLI inputs and outputs are not retained; other Copilot access keeps them up to 28 days; user engagement data is kept two years |
| Your retention | Not applicable (Copilot suggestions not stored in your systems unless developers copy them) |
| Training on data | Business and Enterprise: not used for training. Free, Pro and Pro+: interaction data has been used for training since April 24, 2026 unless the user opts out under Privacy in settings |
| Security measures | Copilot Trust Center lists SOC 2 Type 2, ISO 27001 and ISO/IEC 42001:2023 |
| DPA reference | GitHub Data Protection Agreement, part of the GitHub Customer Agreement |
| Note | The Copilot audit log (Business and Enterprise) records settings, license and agent activity but not the prompts users send locally, and keeps events 180 days. Ask developers not to paste real personal data into Copilot chat |
4. Microsoft 365 Copilot
| Field | Entry |
|---|---|
| Activity name | AI-assisted productivity, Microsoft 365 Copilot |
| Controller | [Your company name] |
| Purpose | Employee productivity, email drafting, document summarization, meeting notes, data analysis |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | Employees; customers (if customer emails or documents are processed) |
| Categories of personal data | Email content, document text, meeting transcripts, calendar data, Teams messages, all may contain PII |
| Processor | Microsoft Corporation (One Microsoft Way, Redmond, WA 98052, USA) [check the Microsoft entity named in your licensing agreement] |
| Third-country transfer | For EU customers, Microsoft 365 Copilot is an EU Data Boundary service, but Anthropic models (a Microsoft subprocessor) are currently excluded from the EU Data Boundary. Safeguard: Microsoft Products and Services Data Protection Addendum |
| Vendor retention | Prompts and responses are stored with your other Microsoft 365 content, under your organization's contractual commitments |
| Your retention | Controlled by the Copilot retention policies you configure in Microsoft Purview |
| Training on data | No. Prompts, responses and Microsoft Graph data aren't used to train foundation LLMs |
| Security measures | Encryption at rest and in transit; Microsoft lists GDPR, ISO 27001, HIPAA and ISO 42001 among Copilot's compliance offerings |
| DPA reference | Microsoft Products and Services Data Protection Addendum, May 2026 edition |
5. Google Workspace AI (Gemini for Workspace)
| Field | Entry |
|---|---|
| Activity name | AI-assisted productivity, Gemini for Google Workspace |
| Controller | [Your company name] |
| Purpose | Email drafting, document summarization, spreadsheet analysis, presentation creation |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | Employees; customers (if customer data appears in Workspace documents) |
| Categories of personal data | Email content, document text, spreadsheet data, Drive files, may contain PII |
| Processor | Google [add the Google entity and address named in your Google Workspace agreement] |
| Third-country transfer | Data regions can keep covered data stored in the EU on supported editions (Business Standard and up, not Business Starter), and Google says Gemini processing can be kept in the EU or US. Safeguard: Cloud Data Processing Addendum (a recognised transfer framework where Google has adopted one, otherwise SCCs) |
| Vendor retention | Gemini follows the data-deletion section of the Cloud Data Processing Addendum; Workspace content follows your own retention settings |
| Training on data | No. Content isn't used for generative AI model training outside your domain without permission |
| Security measures | Gemini holds ISO 42001, BSI C5 and FedRAMP High certifications |
| DPA reference | Cloud Data Processing Addendum, which Google Workspace's DPA link now points to |
6. Notion AI
| Field | Entry |
|---|---|
| Activity name | AI-assisted knowledge management, Notion AI |
| Controller | [Your company name] |
| Purpose | Note taking, document drafting, knowledge base summarization |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | Employees; potentially customers if customer data is stored in Notion |
| Categories of personal data | Workspace content, notes, documents, project data that may contain names, contact details, internal data |
| Processor | Notion Labs, Inc. (685 Market Street, San Francisco, CA 94105, USA) |
| Third-country transfer | Yes, US processing, and Notion AI's model providers (OpenAI, Anthropic) are listed with a "Global" location. Safeguard: Notion DPA with the 2021 SCCs, part of the Master Subscription Agreement that covers Plus, Business and Enterprise plans and any use on behalf of an organization |
| Vendor retention | On Free, Plus and Business, Notion's LLM providers keep data 30 days or fewer. On Enterprise, most models run with zero retention; the few that keep data are off until the workspace owner opts in. Admins can switch on data-retaining models for some features. Embeddings deleted within 60 days of deleting the page or workspace |
| Training on data | No. Notion's AI terms say it doesn't use customer data, or let others use it, to train the models behind Notion AI |
| Security measures | Notion AI is in scope of Notion's SOC 2 Type 2 report and ISO 27001 certification |
| DPA reference | Notion Data Processing Addendum, effective August 14, 2026 |
7. Grammarly (team plans)
| Field | Entry |
|---|---|
| Activity name | AI writing assistance, Grammarly |
| Controller | [Your company name] |
| Purpose | Grammar and style checking for employee-written content |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | Employees; text may contain customer references |
| Categories of personal data | Written content submitted for correction, may contain names, contact details, business-sensitive information |
| Processor | Superhuman Platform Inc., formerly Grammarly, Inc. (USA) |
| Third-country transfer | Yes, Grammarly is hosted on AWS in the US East region. Safeguard: EU-US Data Privacy Framework, with the 2021 SCCs where the Framework doesn't cover the transfer (Superhuman Data Privacy Addendum) |
| Vendor retention | No fixed period published; the privacy policy keeps data "for as long as necessary to provide our products" |
| Training on data | Off by default for Enterprise, Education and plans bought through sales. Multi-user plans bought on the website start with Product Improvement and Training on, and an admin must turn it off |
| Security measures | SOC 2 Type 2 and ISO 27001 (Superhuman DPA security exhibit) |
| DPA reference | Superhuman Data Privacy Addendum, effective July 8, 2026 |
8. HeyGen (AI video generation)
| Field | Entry |
|---|---|
| Activity name | AI video generation, HeyGen |
| Controller | [Your company name] |
| Purpose | [customize], e.g., product demos, training videos, marketing content using AI avatars |
| Legal basis | Legitimate interests (Art. 6(1)(f)); Consent (Art. 6(1)(a)) if using real employee likenesses |
| Categories of data subjects | Employees (if using real likenesses); end viewers if video contains personal data |
| Categories of personal data | Avatar likeness data (if using employee avatar); script text (may contain PII); generated video files |
| Processor | HeyGen Technology Inc. (12130 Millennium Drive Suite 300, Los Angeles, CA 90094, USA). HeyGen says it acts as your processor for inputs and outputs, and as a controller for its own model training |
| Third-country transfer | Yes, HeyGen is hosted on AWS in the United States. Safeguard: SCCs; HeyGen also lists EU-US Data Privacy Framework participation |
| Vendor retention | No fixed period published. HeyGen says it strives to delete data within 72 hours of a deletion request |
| Training on data | Enterprise: excluded from AI training by default. Other plans: HeyGen uses inputs to train its models under its legitimate interests; opt out by emailing [email protected] |
| Security measures | SOC 2 Type II |
| DPA reference | HeyGen says it provides DPAs to controllers (GDPR page); we found no public DPA text, so ask for it before signing |
| Special note | Likeness consent: if any real person's face or voice is used, obtain signed written consent before using. Relevant to Washington's AI likeness law (SSB 5886, effective June 11, 2026) and similar laws. |
9. Intercom AI (Customer Service)
| Field | Entry |
|---|---|
| Activity name | AI-assisted customer service, Intercom Fin AI |
| Controller | [Your company name] |
| Purpose | Automated customer support responses; query routing; conversation summarization |
| Legal basis | Legitimate interests (Art. 6(1)(f)), efficient customer support; or Contract (Art. 6(1)(b)) if AI resolves service requests |
| Categories of data subjects | Customers |
| Categories of personal data | Customer names, email addresses, support conversation content, account identifiers, typically high-PII environment |
| Processor | Intercom, Inc. (55 2nd Street, 4th Fl., San Francisco, CA 94105, USA), or Intercom R&D Unlimited Company (124 St Stephen's Green, Dublin 2) [check the Intercom company on your contract] |
| Third-country transfer | Data hosted in the US, EU or Australia, depending on your choice. Safeguard: the EU-US, Swiss-US and UK-US Data Privacy Framework; the 2021 SCCs (Module Two or Three) apply if the Framework stops covering the transfer |
| Vendor retention | [Confirm with Intercom: we found no published default period for conversation data]. Fine-tuning data is deleted within 30 days of an opt-out |
| Training on data | Yes, unless you opt out: Fin can use anonymized customer data for model fine-tuning. Third-party AI providers are contractually barred from training on your data and keep none once an output is generated |
| Security measures | SOC 2 Type II, HIPAA, ISO 27001, ISO 27018, ISO 27701 and ISO 42001 |
| DPA reference | Intercom Data Processing Addendum, effective April 9, 2025 |
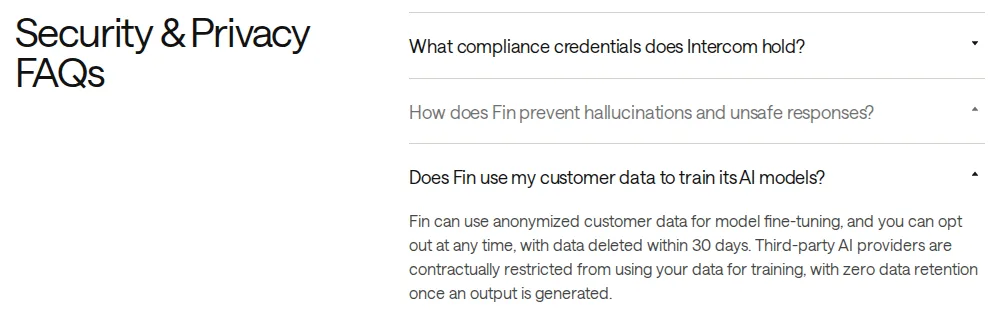
Screenshot: Security and Privacy FAQs, intercom.com/security, checked October 16, 2026.
10. AI Hiring Tools (Recruitee and similar)
| Field | Entry |
|---|---|
| Activity name | AI-assisted candidate screening, [Tool name] |
| Controller | [Your company name] |
| Purpose | Resume screening; candidate ranking; interview scheduling |
| Legal basis | [customize]. Screening with real human review can rest on legitimate interests (Art. 6(1)(f)) or on steps taken at the candidate's request before entering a contract (Art. 6(1)(b)). A decision based solely on automated processing with legal or similarly significant effects is allowed only if necessary for a contract, authorised by law, or based on explicit consent (Art. 22(2)) |
| Categories of data subjects | Job applicants |
| Categories of personal data | Names, CVs, cover letters, contact details, interview notes, potentially protected characteristics (age, gender implied by names/dates) |
| Processor | [AI hiring tool vendor name and address] |
| Third-country transfer | [Confirm with vendor] |
| Vendor retention | [Confirm with vendor, candidates have access rights] |
| Training on data | [Confirm with vendor, critical for bias risk] |
| Security measures | [Vendor security documentation] |
| DPA reference | [Vendor DPA] |
| GDPR Art. 22 note | If candidates can be rejected automatically by AI without meaningful human review, Art. 22 applies. Your privacy notice must say so (Art. 13(2)(f)), and for contract or consent cases you must offer at least the right to human intervention, to express their point of view and to contest the decision (Art. 22(3)). |
11. Salesforce Einstein (CRM AI)
| Field | Entry |
|---|---|
| Activity name | AI-assisted CRM, Salesforce Einstein |
| Controller | [Your company name] |
| Purpose | Sales forecasting, lead scoring, email writing assistance, opportunity insights |
| Legal basis | Legitimate interests (Art. 6(1)(f)) |
| Categories of data subjects | Customers; prospects; partners |
| Categories of personal data | Customer names, contact details, deal history, communication content, behavioral data |
| Processor | Salesforce, Inc. (415 Mission St., 3rd Floor, San Francisco, CA 94105, USA) |
| Third-country transfer | The Hyperforce EU Operating Zone (launched March 2, 2023) lets you store and process data in the EU. Safeguard: Salesforce DPA transfer mechanisms: Salesforce Processor Binding Corporate Rules for covered services, SCC Module 2 and SCC Module 3 |
| Vendor retention | Set by your own Salesforce data retention configuration; under the Einstein Trust Layer's zero data retention policy, third-party LLM providers don't store prompts or responses |
| Training on data | Under the Einstein Trust Layer, prompts and generated responses are never used to train the underlying third-party large language models |
| Security measures | ISO 27001 certifications and SOC 2 reports per service, as listed in Salesforce's Security, Privacy and Architecture Documentation (compliance.salesforce.com) |
| DPA reference | Salesforce Data Processing Addendum, Revision August 2026 |
12. Midjourney (AI image generation)
| Field | Entry |
|---|---|
| Activity name | AI image generation, Midjourney |
| Controller | [Your company name] |
| Purpose | [customize], e.g., marketing image creation, presentation graphics |
| Legal basis | Legitimate interests (Art. 6(1)(f)), if no personal data in prompts |
| Categories of data subjects | Employees (if prompts contain employee details); depicted individuals (if prompts reference real people) |
| Categories of personal data | Prompt text (only personal data if prompts contain PII or references to real individuals); generated images (personal data only if depicting real people) |
| Processor | Midjourney, Inc. (611 Gateway Blvd. Ste 120, South San Francisco, CA 94080, USA). Its terms and privacy policy don't describe it as acting as your processor |
| Third-country transfer | Yes, data may be processed outside your country. Midjourney's privacy policy says it uses the European Commission-approved SCCs for EEA, Swiss and UK data shared with third parties |
| Vendor retention | Kept as long as necessary for the privacy policy's purposes. By default your content is publicly viewable and remixable; Stealth Mode (Pro and Mega plans only) keeps images and videos private |
| Training on data | The terms give Midjourney a perpetual, irrevocable license to your prompts and outputs, and we found no training opt-out. Stealth Mode controls visibility, not training |
| Security measures | [Not published on the Midjourney pages we checked] |
| DPA reference | We found no DPA on Midjourney's documentation site. Treat Midjourney as unsuitable for personal data unless it signs one with you |
| Risk note | Do not include personal data in Midjourney prompts on consumer or shared accounts. Do not generate images depicting real, identifiable individuals without consent (relevant to Washington likeness law and similar state laws). |
Completing Your RoPA: What Comes Next
After filling in entries for each AI tool:
- Review data subject rights implications
For each AI tool entry, confirm you can fulfil subject access requests (SARs). If a data subject asks for all their personal data, can you retrieve what was sent to each AI tool? If not, your data flows need improvement before your RoPA is complete.
- Add your DPA references
For each AI tool, confirm you have a signed DPA. If any tool lacks a DPA and processes EU personal data, either sign one or stop using that tool for personal data. The RoPA without a DPA is incomplete.
- Check your consent records for high-risk processing
For hiring tools (Art. 22) and any special category data (health, biometrics) processed through AI, add a column confirming the consent or other legal basis is documented separately.
- Review retention in both directions
Your RoPA must document both your retention period and the AI vendor's retention period. If your vendor retains data for 30 days and you retain for 2 years, your RoPA should reflect both, and you should consider whether the vendor's 30-day period creates a gap in your ability to respond to SARs.
- Update annually at minimum
AI tool landscapes change fast. DPAs get updated, vendors add new sub-processors, and data residency options expand. Review your AI RoPA entries at least annually or when you add a new AI tool.
What This Template Doesn't Cover
It's the controller's record only. Your vendors keep their own processor records under Article 30(2), and a DPIA, if the processing needs one, is a separate document.
What we could not confirm on October 16, 2026: the Google entity and address for Workspace contracts (it depends on your agreement), the full text of Microsoft's DPA (the download didn't open for us, so we cite the DPA page), HeyGen's DPA text (heygen.com/dpa returned a 404), Intercom's default retention for conversation data, and whether Midjourney will sign a DPA at all. Those cells tell you what to ask for.
This template is for reference; have your DPO or legal counsel review it before relying on it for compliance.
Correction (October 16, 2026): The Notion AI and Grammarly entries gave an old address for Notion and Grammarly's former company name, pointed to privacy pages instead of the DPAs, limited Notion's DPA to Business and Enterprise, said Notion AI queries are kept 30 days, and said Grammarly Business data isn't used for training. Notion's DPA covers Plus, Business, Enterprise and any organization use, and its model providers keep data 30 days or fewer (none on Enterprise). Grammarly team plans bought on its website start with training on until an admin turns it off. Both entries now link the current DPAs.
Correction (October 16, 2026): A later check of the other ten entries found more errors. OpenAI's DPA party is OpenAI OpCo, LLC at 1455 3rd Street (OpenAI Ireland Ltd. for EEA and Swiss customers), not OpenAI, L.L.C. at 1960 Bryant Street, and EEA, Swiss and UK customers contract with Anthropic Ireland, Limited. GitHub Copilot Free, Pro and Pro+ data has trained GitHub's models since April 24, 2026 unless users opt out. Intercom can fine-tune on anonymized customer data and HeyGen trains on non-Enterprise inputs unless you opt out; both entries said the opposite. HeyGen's company is HeyGen Technology Inc. in Los Angeles, not HeyGen Interactive in San Francisco. Midjourney's Stealth Mode controls visibility, not training, and we found no Midjourney DPA. Salesforce's training line now quotes its Trust Layer. Washington's likeness law took effect June 11, 2026, not June 10. The Article 30 notes now quote the ICO instead of an EDPB claim we couldn't source, and call the AI vendor a processor rather than a sub-processor.
Correction, October 22, 2026: the Notion AI entry said Enterprise has zero retention at its LLM providers. Notion's AI security page now says most Enterprise models have zero retention and a small number do not; those are off by default until the workspace owner opts in. The vendor retention row now says so.
Related Reading
- ICO agentic AI call for evidence: what 10 AI developers changed
- AI vendor DPA tracker 2026, DPA and training status by plan
- Anthropic vs OpenAI GDPR compliance differences
- AI vendor due diligence checklist 2026
- AI governance guide for small teams
- Privacy-first AI APIs, which vendors don't train on your data
- AI acceptable use policy template
- ChatGPT Memory Upgrade (Dreaming V3): What It Means for Business Privacy
- GDPR-Compliant AI Assistants: Claude, ChatGPT Enterprise, Gemini, and Mi
- OpenAI API governance and data privacy for developers 2026
